❌

Reading view

Switch 2 security takes a hit as hackers unlock homebrew access

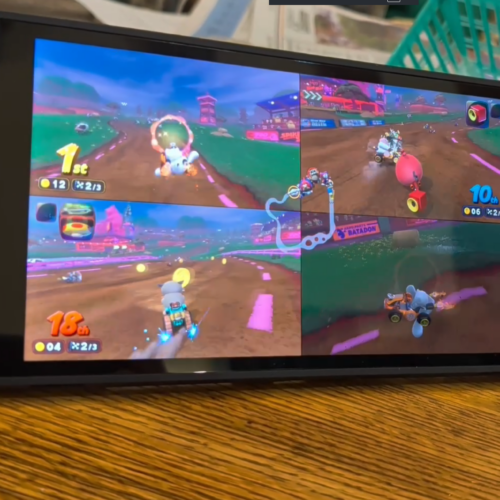
A security researcher has demonstrated a software-only partial jailbreak of the Switch 2, gaining "userland" access that he says "lets us run homebrew, reverse engineer and mod Switch 2 games, back up save files off the Switch, and access most of the Switch 2’s peripherals through MMIO."

The hack relies on the original Switch version of SmileBasic 4, the latest in a long-running series of programming environments and interpreters that run on Nintendo hardware. The so-called "tethered" hack also requires access to a macOS or Linux PC on the same network to run a node.js package that helps enable privileged system access.

Researcher Sammy Hajhamid writes that he used OpenAI's Codex to poke at SmileBasic's language interpreter, using a custom harness that could send USB commands to the system and view results via HDMI (as well as power cycling via a Bluetooth light switch flipping device). After "substantial effort for ~2 weeks," that harness discovered a 32-bit integer overflow that occurs when removing items from an array in SmileBasic. That error gives access to an array pointer, which in turn allows read-and-write access to portions of system memory.

Read full article

Comments

© Pepsipu.com

  •  

Hackers got a four-day head start on epic PHP2Shell vulnerability

Amazon has warned that vulnerabilities in a programming language that underpins much of the Internet, discovered using AI tools, are being “broadly exploited” as governments and companies rush to secure their systems.

The world’s largest cloud computing provider on Wednesday said it had identified an attempt by hackers to exploit the bug four days before the weakness was disclosed to the public.

Amazon added the flaws were “now being broadly exploited in the wild.”

Read full article

Comments

© Getty Images

  •  

333 Tor exit nodes hijacked to intercept SSH traffic and retrieve plaintext email

Unknown hackers hijacked more than 300 Tor exit nodes and reconfigured them to favor unencrypted email traffic and redirect SSH connections through servers they controlled, a researcher reported Tuesday.

The hijacking began in late August, when, according to Tor volunteers, the attacker used a valid password that had been reused to gain access to a Tor management server. The attacker then installed Ebury, a backdoor written for Linux that was discovered 12 years ago.

Mysteries remain

Then the attacker connected from the management server to a second Tor server, called Switzerland2, through SSH, using an RSA key that, for unknown reasons, investigators couldn’t find among Switzerland2’s authorized keys. With administrative control of Switzerland2, the attackers installed Ebury there as well. Finally, the attacker reconfigured settings on two exit nodes that Switzerland2 hosted.

Read full article

Comments

© Photo Illustration by Pavlo Gonchar/SOPA Images/LightRocket via Getty Images

  •  
❌