❌

Reading view

Drones sink ships near NATO countries in “unacceptable” attacks, EU says

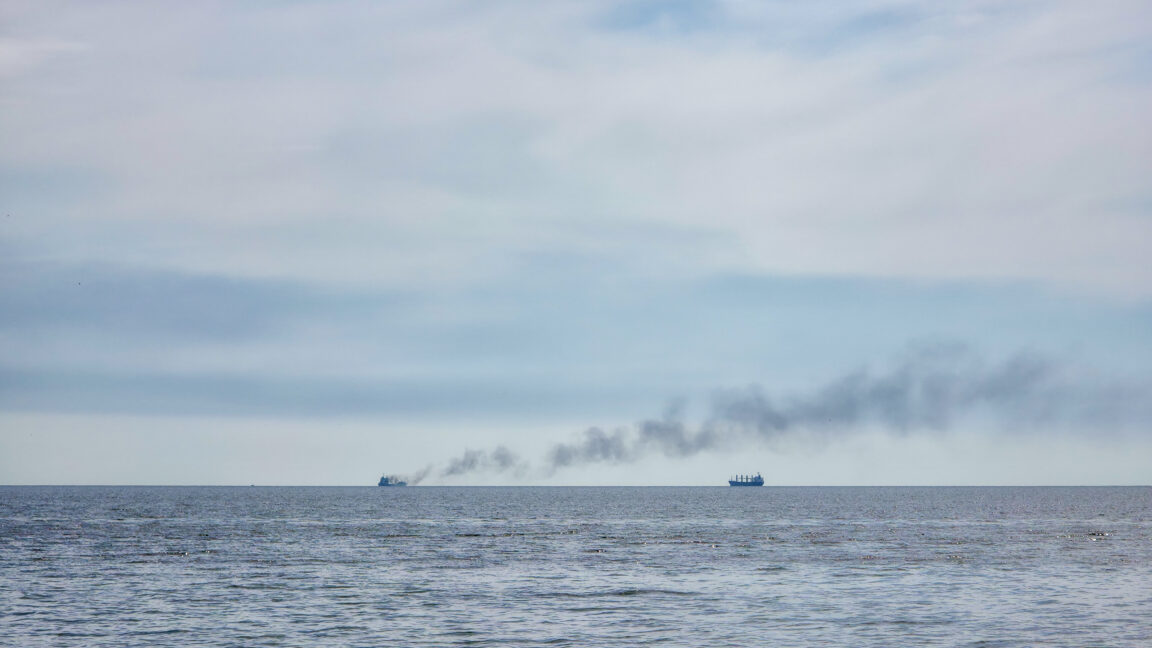
Drones sank two cargo ships and damaged a third in the exclusive economic zones of NATO member countries for the first time, killing at least two sailors. The attacks represent a notable escalation as Black Sea commercial shipping has increasingly come under attack during the Russian invasion of Ukraine, with Russia also being accused of carrying out “hybrid warfare” incidents across Europe.

The Togo-flagged cargo ship Alfa Watan sank, and the Palau-flagged cargo ship Able was set ablaze after being attacked by multiple sea and aerial drones about 80 miles (128 kilometers) off the coast of Bulgaria on October 6, according to the Associated Press. In an interview, Bulgarian Prime Minister Rumen Radev described the incidents as “an unacceptable attack in Bulgaria’s exclusive economic zone” and “a blatant violation of international law and maritime law.”

A Bulgarian ferry managed to evacuate the 18 crew members of the Able, with two severely injured mariners being flown to a hospital in the city of Varna.

Read full article

Comments

© Iuliia Kuzmina / iStock Editorial / Getty Images

  •  

OpenAI will watermark ChatGPT outputs by default—but only in the EU

OpenAI will begin automatically watermarking text generated with ChatGPT in the European Union, the company has announced. It will also offer the watermarking feature in other regions, but it will be off by default outside of the EU.

The move in Europe is driven by a need to comply with the EU AI Act, which took effect in August. It requires marking content produced by AI models in a way that another tool can detect. Unfortunately, there is still no completely effective and reliable way to do that. A few standards already exist, like SynthID and the C2PA project, but they are relatively easy to circumvent for anyone with basic know-how.

The same is likely true for OpenAI's watermark. Its method is proprietary; the company calls it textGrain, and has published a technical paper explaining how it works. But in general, it works like other LLM watermarking tools we've seen in the past: It puts patterns in the word choices that are not clear to a human reader and that don't meaningfully change the general quality of the output, but that someone with a key can use a specialized detector to find. OpenAI says it will be giving access to the detector to a limited number of researchers and organizations and providing a request-for-approval process for others to be added over time.

Read full article

Comments

© Getty Images | NurPhoto

  •  

HBO Max, Paramount+, and Discovery+ "will unify into a single service”

After months of industry and customer speculation, Paramount Skydance has shed some light on the future of the HBO Max and Paramount+ streaming services.

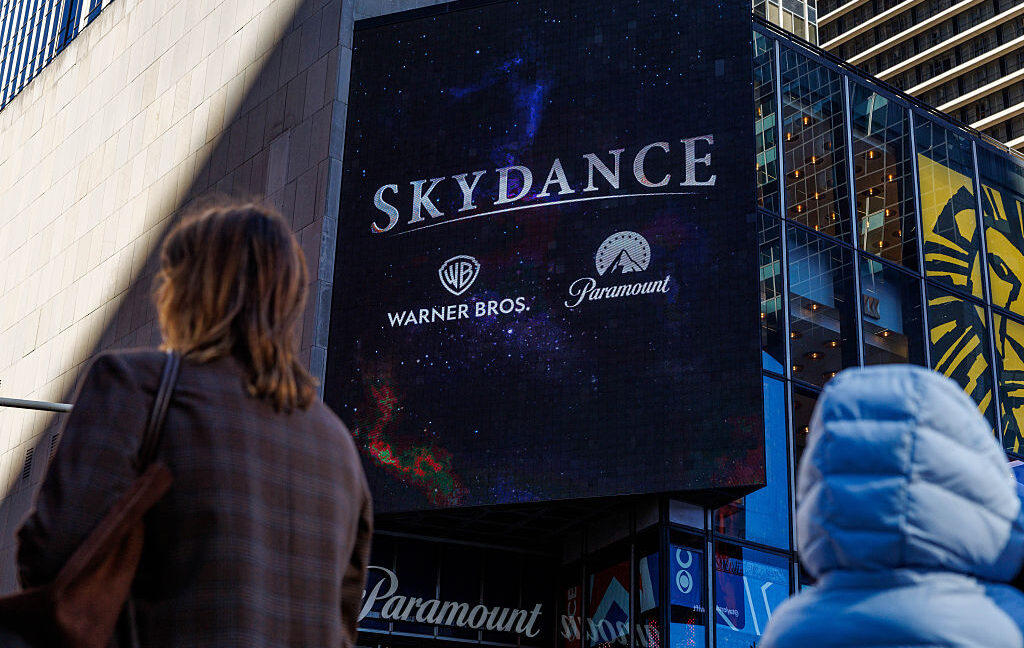
Paramount Skydance completed its acquisition of Warner Bros. Discovery (WBD) today, ending a monthslong saga that began when Netflix last year announced its own plans to buy WBD. Netflix scrapped those plans in February. Skydance is the name of the company created from the $111 billion merger.

In an announcement today, Skydance said that all of the direct-to-consumer streaming services it owns, including the Discovery+ service that Discovery Inc. (which merged with WarnerMedia in 2022 to create WBD) launched in 2021, “will unify into a single service over time.”

Read full article

Comments

© Adam Gray/Getty Images

  •  

It looks like the Atlantic storm season may finally produce a hurricane

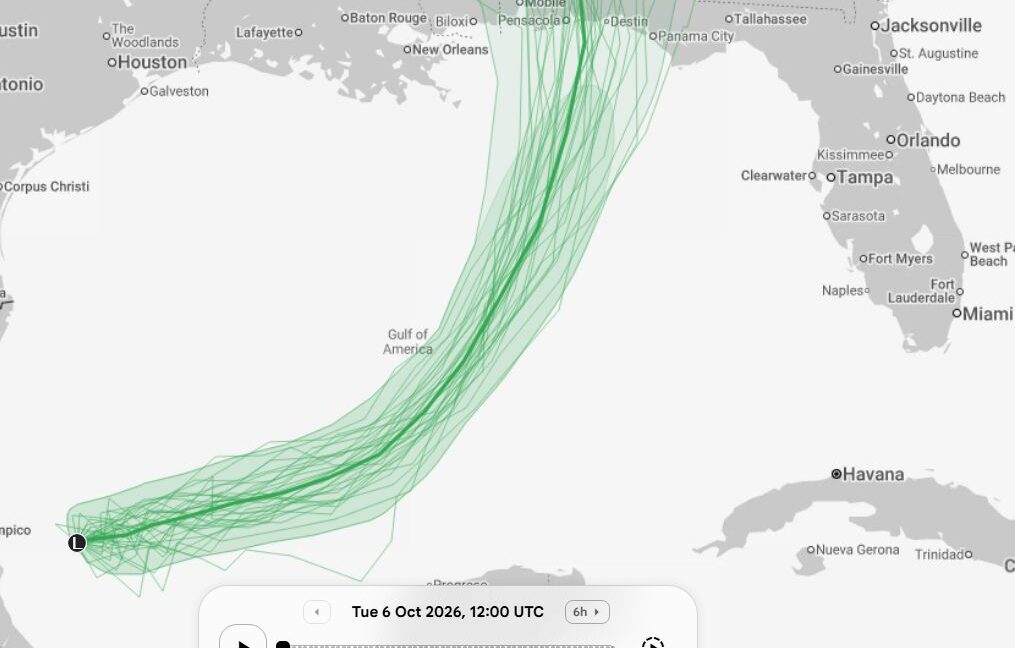
A low-pressure system in the western Gulf of Mexico should soon become a tropical storm, and based on the latest forecast modeling, it has a decent chance of becoming a hurricane.

Normally, a hurricane forming in early October would not be particularly noteworthy. However, this year the development of a hurricane would be a big deal—because it has not happened yet.

In the modern hurricane record—an era dating to about World War II when there has been aircraft reconnaissance and later continuous satellite coverage—there has never been an Atlantic season without a hurricane, and no season has gone this late without one forming.

Read full article

Comments

© Google Weather Lab

  •  

Hackers obtain counterfeit TLS certificates for Google and other large services

Attackers hijacked three top-level domains and used their control to mint counterfeit TLS certificates for Google and other large organizations, Google said Tuesday.

The attackers launched a series of attacks on the .gh, .sl, and .as country code top-level domains (ccTLDs) and then modified authoritative DNS records for selected domains within those namespaces. By controlling those DNS records, the attackers were able to pass automated domain control validation checks and obtain unauthorized certificates for “several Google domains” and “several leading global brands and widely used online services.” Google said it updated Chrome to block all certificates it identified as unauthorized, and worked with the issuing certification authorities to ensure the unauthorized certificates for Google properties were revoked.

Certificate issuance: The weak link in the chain

TLS certificates are the cryptographic credentials that underpin authentication and encryption protections for websites, mail servers, and other Internet infrastructure. These x.509 certificates use a digital signature to bind a domain name such as google.com to a public key. The public key is publicly available, while the private key is held only by the website operator. When a connection shows that the keys match, the visiting party knows it’s connected to the authentic site rather than an impostor. Possession of unauthorized certificates allows attackers to cryptographically impersonate the affected infrastructure.

Read full article

Comments

© Getty Images

  •  

Paramount completes $111B Warner merger, creating “Skydance” behemoth

Paramount Skydance completed its $111 billion merger with Warner Bros. Discovery today, after a last-ditch effort to block the deal was rejected by Supreme Court Justice Elena Kagan.

The post-merger company is called Skydance, taking the name of a firm that Paramount bought in a separate deal last year. The new Skydance combines two of the largest movie studios, streaming services Paramount+ and HBO Max, CBS, CNN, "and a portfolio of live sports including CBS Sports and TNT Sports, as well as a deep programming library and expansive collection of brands and franchises," Skydance said today in a press release announcing completion of the deal.

The merger was delayed a bit by a lawsuit filed by California and 11 other states. In July, US District Judge Araceli Martínez-Olguín in the Northern District of California ruled that the combination would likely reduce competition substantially and violate antitrust laws.

Read full article

Comments

© Getty Images

  •  

Support Ars and get a better reading experience in return

When Ars launched in 1998, there was one way to read it: in a web browser on a PC (or Mac). Your screen of choice was either some massive CRT or a very expensive LCD monitor (or, in my case, the less-expensive grayscale, passive-matrix LCD on a PowerBook). Either way, it was butt in chair, chair at desk.

One of the first perks we offered subscribers way back at the turn of the millennium allowed them to read Ars without a browser. Articles were available as formatted PDF files, so you could print out John Siracusa's Mac OS X Public Beta review and read it on the subway or build your own searchable archive of your curated Ars content. Another option was full-text RSS feeds—instead of getting a two-paragraph summary, subscribers could browse Ars in their favorite RSS reader.

It's 2026, and while screens have proliferated in size and portability, ArsPro subscribers still get PDFs of every article and full-text RSS feeds, because sometimes the web isn't always the ideal place to read the web.

Read full article

Comments

© Aurich Lawson | Getty Images

  •  

Amazon kills Alexa’s ability to control Echo speakers' AUX input

Amazon has disabled Alexa control of devices plugged into the company's Echo smart speaker’s AUX port.

Users have reported receiving an email from Amazon this week informing them of the change. “This is a reminder that as of today, voice commands to control your Echo device’s Aux input are no longer available. Requests like 'Alexa, play from line in” or “Alexa, set aux input' will no longer work,” an email that Amazon sent reads, according to a screenshot a Reddit user shared this week.

An Amazon spokesperson confirmed the news to Ars Technica today.

Read full article

Comments

© Amazon

  •  

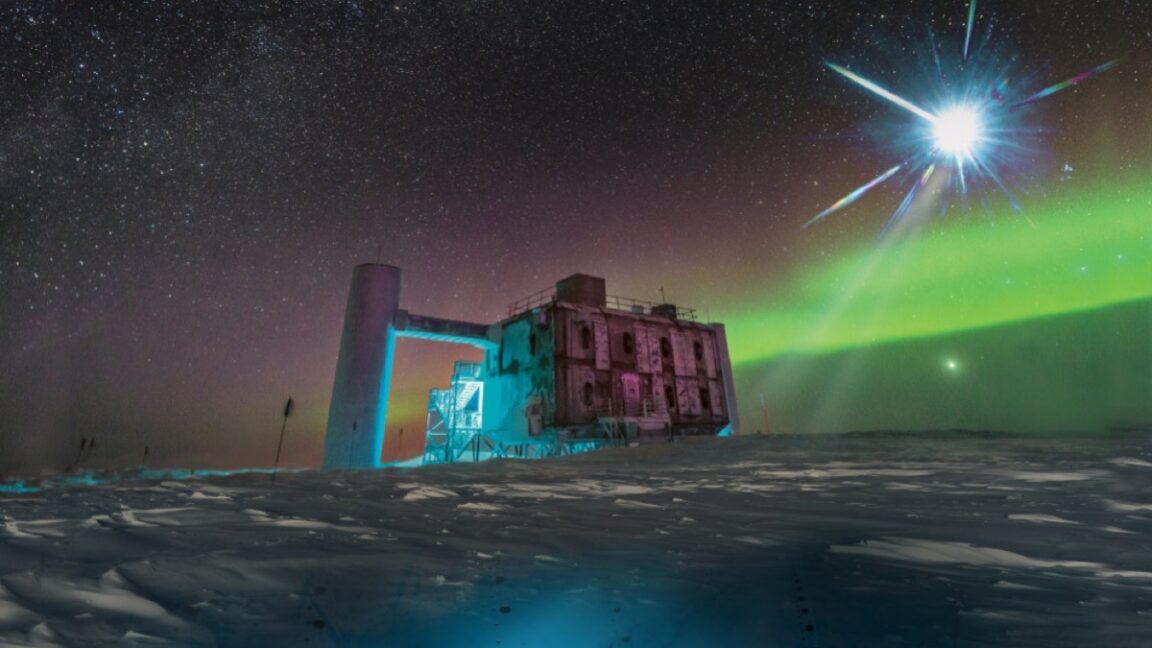
Neutrino physicist wins 2026 Nobel Physics Prize

Francis Halzen, a physicist at the University of Wisconsin, Madison, has won the 2026 Nobel Prize in Physics "for decisive contributions to the IceCube Neutrino Observatory and the discovery of high-energy neutrinos of astrophysical origin.” Halzen spearheaded the development and construction of the IceCube Neutrino Observatory in Antarctica, enabling physicists to capture high-energy neutrinos created in the distant universe.

“It was a great surprise, and I obviously didn’t expect it,” Halzen said during a news conference in Stockholm, Sweden, speaking by phone from Italy. While the Nobel was awarded to Halzen, he emphasized that his work was the result of a “large collaboration” with other researchers.

“This reflects on the really courageous people who joined me in this project when really no respectable conservative physicist would have joined me. But many talented people did, and that’s why I’m here,” he said.

Read full article

Comments

© IceCube/NSF

  •  

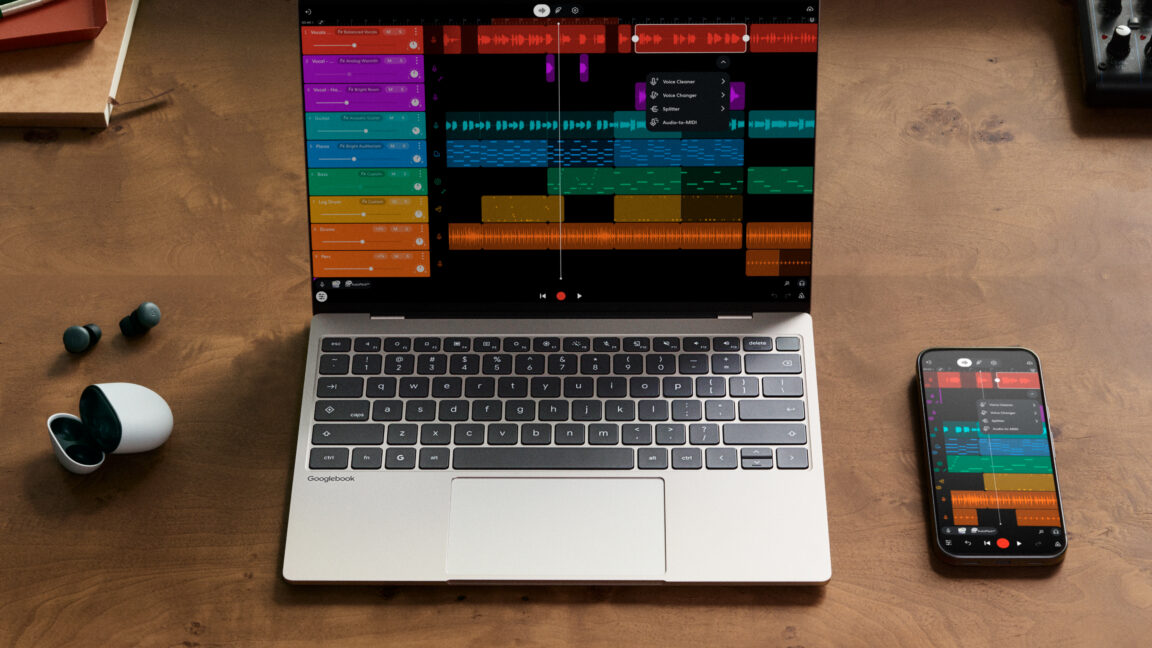
Googlebook "Better Together" phone features don't work with Samsung at launch

Googlebooks are Google's latest attempt to carve out a piece of the premium laptop market, and tight integration with Android phones is a key part of that effort. Now that Googlebooks are available, we're learning of some frustrating limitations of that plan. For now, Googlebooks will only play nicely with your phone if you have a Pixel.

When Google announced the launch window for Googlebooks, it said the laptops were "engineered to work with your Android phone right out of the box." But as with many things Google, the truth is more convoluted. We have since learned that you need Android 17 for any of the nifty integrations to work. With a compatible Android 17 phone, you can seamlessly stream apps to your laptop, access files on your phone, mirror notifications, and continue where you left off in certain apps when switching from phone to laptop.

You might think that the latest Samsung phones, which shipped with Android 17, would be ready for this experience. You'd be wrong, though. Some early Googlebook adopters have complained that phones like the Z Fold 8 won't work with the laptops. While the devices appear to see each other, the phone doesn't stay connected. Google representatives have since confirmed that these "Better Together" features are not currently supported on even the latest Samsung phones. An update that brings support to Samsung phones will roll out in "the coming weeks."
Read full article

Comments

© Google

  •  

FreshRSS 1.30.1

This is a security-oriented release with several security patches and bug fixes in the continuation of 1.30.0.

Note that our rolling-release channel (edge) is recommended for faster security patches.

Bug fixes highlights 🐛:

  • Some security attack scenarios patched
  • Fix domain-wide Retry-After
  • Fix muting of feeds gone with HTTP 410

Feature highlights✨:

  • CLI: Add optional feed argument to actualize-user.php

This release has been made by @Alkarex, @andris155, @fzlzjerry, @Inverle, @jamalkamaladdin, @jtracey, @Otolock and newcomers @akine, @colons, @ethanstoner, @gigioneggiando, @Juice-de-Orange, @pavel-miniutka, @qwist1233-cpu, @Sharawey74, @shcheglovnd, @TapuGithub, @yuchenshi, @ZainnQureshii

Full changelog:

  • Deployment
    • Reword recommendations and explanations for edge (rolling release) vs. latest (versioned release) channels #9270
  • Security
    • Config + increase default values for search max length and depth #9280
    • Accept a trusted proxy address given without a subnet #9301
    • Warn during session regenerate fail #9311, #9376
    • CI/CD add zizmor workflow for action security checks #9228, #9331
    • Use PHP #[\SensitiveParameter] #9322
    • Reject token access (RSS/OPML export, feed refresh) for disabled accounts #9336
    • Require POST+CSRF for self-update mutations #9335
    • Make the login challenge nonce one-time #9334
    • Bound ZIP import against decompression bombs #9332
    • Rotate session ID on all authenticated transitions #9333
    • Minz: Remove vulnerable and unused code path for displaying errors #9395
    • Fix NAT64 feed fetching on IPv6-only hosts #9372
  • Bug fixes
    • Fix domain-wide Retry-After #9390
    • Fix muting of feeds gone with HTTP 410 #9391
    • Fix infinite redirect loop due to SCRIPT_NAME in PATH_INFO #9282, #9287
    • Restore the automatic reading view after marking articles as read, while preserving explicit filters #9288
    • Fix adaptive reading state after marking articles read #9290
    • Fix regression sharing links #9303
    • Don’t disable anonymous refresh when anonymous feed access is disabled #9354
    • Fix regression with HTTPS proxies due to wrong TLS SNI resolution #9341
    • Better enforce limits for feeds and categories #9357
    • Fix JavaScript error when opening a label menu in sidebar #9377
    • Fix custom favicon with GReader API #9409
  • CLI
    • Add optional feed argument to actualize-user.php #9319
  • UI
  • Extensions
    • Call check_url_before_add hook when previewing a feed #9343
  • I18n
  • Misc.

  •  

FreshRSS 1.30.0

This is a security-oriented major release with several important security patches, so users are encouraged to update without delay.

From this release, we are also making it clear that our rolling-release channel (edge) is recommended for faster security patches.

Breaking change 💥:

  • Disallow access to local networks such as 127.0.0.1 by default, for security reasons

Feature highlights✨:

  • Filter global view feed list by state and search
  • New option to hide badges showing number of unread articles (Phantom Obligation)
  • Refresh only feeds in the current view
  • Offer to add a prefix when re-sharing user labels

Bug fixes highlights 🐛:

  • Several security attack scenarios patched
  • Fix lost elements while parsing search query
  • Fix “mark as read older than…” widening the active search
  • Fix saving user queries
  • Fix SQL errors breaking some regex searches with MySQL / MariaDB

This release has been made by @Alkarex, @andris155, @ColonelMoutarde, @Frenzie, @IEEE-754, @Inverle, @math-GH, @nykula, @polybjorn, @Stunkymonkey and newcomers @0xdeadrelay, @AdamKorcz, @aligundogar, @bossaarebecca-alt, @Cactys12, @chrislongros, @Divinelink, @Elgeryy1, @featurecreep-cron, @Fripix, @fzlzjerry, @georatas, @gshimo, @iatman ,@ihsanarifr, @jamalkamaladdin, @JamBalaya56562, @jbrayton, @jeremy-code, @juherr, @kobihikri, @LeeXiaolan, @masskrdjn, @mohammadlashkari, @nathanpixodeo, @Otolock, @payaci, @salvador-castro, @SamCyber001, @satyvm, @senti-man, @simitana, @ThomasVermeer, @Totara-thib, @TowyTowy, @utkutibet, @XiaoSong1223

Full changelog:

  • Security
    • 💥 Disallow access to local networks such as 127.0.0.1 by default, for security reasons (breaking change) #8400,
      #9195
      • Selected local networks can be allowed under System configuration or using the INTERNAL_HOST_ALLOWLIST environment variable
      • Passing * allows all networks like before (unsafe)
    • Improve SSRF mitigations by restricting CURLOPT_PROXY #8950
    • Fix auth CSRFs (login and register actions) #9171
    • Log invalid challenge and ignore JSON error during login #9278
    • Disallow fetching of non remote URI #9215
    • Only allow HTTP/HTTPS schemes for enclosure and thumbnail URLs #9272
    • Fix access control in rss and opml actions #8912
    • Refactor to use CSRF field directly instead of borrowing it from a form #9169, #9205
    • Cleaner limit anonymous mode to default user #9235
    • Fix HTML ingestions in templates #9146, #9170
    • Fix bad header filtering bypass #8964
    • Sanitize all fields during JSON import #9168
    • Gate greader (JSON) user query share format behind Share by OPML #9248
    • Public OPML should not contain cURL parameters #9070
    • Ignore security-relevant OPML attributes for dynamic OPML sources #9276
    • Strip feed URL credentials from anonymous user query output #9246
    • Set limits for regex during search #8913
    • Fix path disclosure in cache error message #9206
    • Limit the length and parentheses nesting depth of a search query #9277
    • Use timing-safe comparison for tokens #8945
    • Use hash_equals() for GReader API token comparison #9183
    • Mailer: allow disabling SMTPAutoTLS via config #9026
    • Warn during install if document root does not point to ./p/ #9010
    • Stop the unread-count poller after the session ends #9065
    • Add remote IP address to warning on form login #8942
    • Pin the GitHub actions using SHA #9200
    • Harden cache and SimplePie cache deserialization #9273
  • SimplePie
    • Security: Disallow javascript: URI scheme (protocol) #8263
    • Fix wrong player parent logic leading to invalid type #8893, simplepie#978
    • Consistently enable XML_OPTION_PARSE_HUGE #8894, simplepie#977
    • Fix null warning in IRI for PHP 8.5+ #8918, simplepie#979
    • Fix sanitizer whitelist stripping order #9066
    • Show only one representation per media:group #9009
    • Bump upstream SimplePie #8947
  • Features
    • Filter global view feed list by state and search #9132
      • Use global view when searching from subscription page #9144
    • New option to hide badges showing number of unread articles (Phantom Obligation) #8844
    • Refresh only feeds in the current view #9060
    • Offer to add a prefix when resharing user labels #9236
    • Add log search to the logs page #9059
    • Add configurable log_level system setting #9185
    • New option to keep or not the custom sort order when navigating between categories and feeds #8969
    • New per-feed option to show or hide enclosures (attachments) #9015
    • Detect JSON feeds from URLs containing json #9058
      • Also when subscribing via the API #9167
    • Order categories during OPML import/export according to position #9203
    • OPML: include each feed’s refresh interval (TTL) in export/import #8982
    • Log failed CSS content retrieval (Web scraping) #9077
    • Allow providing a category when adding a feed by bookmarklet #9047
    • Add LinkAce sharing service #9024
    • Add Nextcloud Bookmarks sharing service #9032
  • Bug fixing
    • Fix lost elements while parsing search query #8884
    • Fix “mark as read older than…” widening the active search #9173
    • Fix saving user queries #9190
    • Fix SQL errors breaking some regex searches with MySQL / MariaDB #9036
    • Fix marking filtered label articles as read in SQLite and PostgreSQL #9264
    • Fix tagging an already-tagged entry on PostgreSQL raising a SQL error instead of being a no-op #9136
    • PostgreSQL: make committing new entries resilient to duplicate keys #9231
    • Preserve negative timezone offsets in date intervals #9071
    • Fix feed dropdown bugs due to hash desync #8949
    • Fix slider not reinitializing after form submit #8973
    • Minz: Skip loading duplicated JS/CSS assets #9000
    • Respect simplepie_syslog_enabled for the uses cache logs #8986
    • Fix statistics repartition averages #8996
    • Fix article hover date visibility #8997
    • Keep search and state filters when marking articles as read #9007
    • Fix --db-prefix silently drops following CLI flags #9042
    • Remove stale dynamic favicon links #9127
    • Fix desync between favicon and title unread counters #9262
    • Fix outdated username length hint on registration and install forms #9013
    • Redirect away from wrong URL paths #9075
    • Fix auto-share shortcut on first use #9072
    • Exclude hidden feeds from global view counts #9152
    • Fix only the last <media:credit> being written to the RSS output #9174
  • CLI
    • New cli/reconfigure-user.php to read/write per-user config attributes #8873
    • Report new articles count per feed in app/actualize_script.php output #8948
    • Output a diagnostic when the cli/health.php check fails #8980
  • API
    • Add a warning message to the API password section and a log warning when a client uses GET instead of recommended POST #8845
    • Fever API: log the client IP address on authentication failure #8981
    • WebSub: ignore HTTP/HTTPS scheme difference in Self URL comparison #9005
  • Deployment
    • Docker alternative image updated to Alpine 3.24 with PHP 8.5.7 and Apache 2.4.67 #8916
    • Start supporting PHP 8.6+
      • Docker dev :newest with PHP 8.6 #9155
    • Docker: attach provenance and SBOM attestations to the published image #9150
    • Apache use only CONN_REMOTE_ADDR in logs when mod_remoteip is available, for compatibility with LiteSpeed Web Server #8890
    • Fix .dockerignore being ignored during build in CI #9001
    • New ENABLE_ACCESS_LOG environment variable to disable access logs #9191
    • Check GMP during 32-bit installation #9046
    • Improve actualize mutex to allow multiple instances #9045
    • OIDC: redirect to a default URL on expired auth state instead of 400 #9143
  • UI
    • Always jump article to top when header is offscreen, also when Stick the article to the top when opened is disabled #8870
    • Move article header/footer options (feed title, authors and date, icons position, tags) from Reading to Display configuration #9139
    • Move disable button before remove button in user management #8944
    • Keep scroll position of slider after form submit #8974
    • Group export feeds by category #9079, #9154
    • Sort feed names with locale-aware collation #8985
    • Sort labels with locale-aware collation #9023
    • Format unread counter in title on page load #9263
    • Display slider after submit for all buttons in feed update UI #8999
    • Improve aside keyboard navigation #9202
    • Allows usage of Ctrl/Shift keys with the open website shortcut #9186
    • Fix padding for .nav_menu in Alternative-Dark, Flat, and Nord themes #8901
    • Fix typo in alert error border color variable #9266
    • Use JavaScript Event() constructor instead of deprecated initEvent() #9035
    • Use :user-invalid instead of :invalid for CSS form field styling #9025
    • Remove unused simple layout #8998
    • Various UI and style improvements: #8823, #8824,
      #9140, #9145
  • Extensions
    • Minor Minz_Extension typing #8952
    • Improve extension list fetch diagnostics #9055
    • Fix a PHP warning in Serve action #9267
    • Fix extension settings cancel action #9053
    • Fix sharing menu conflicts with extensions #9074
    • Add read status hook for entries #8995
    • Dispatch a new JavaScript event freshrss:entryStateChange when an entry finishes being marked read/unread #9031
    • Redirect after saving user CSS/JS so changes apply immediately #9006
  • I18n
  • Misc.

  •  
❌