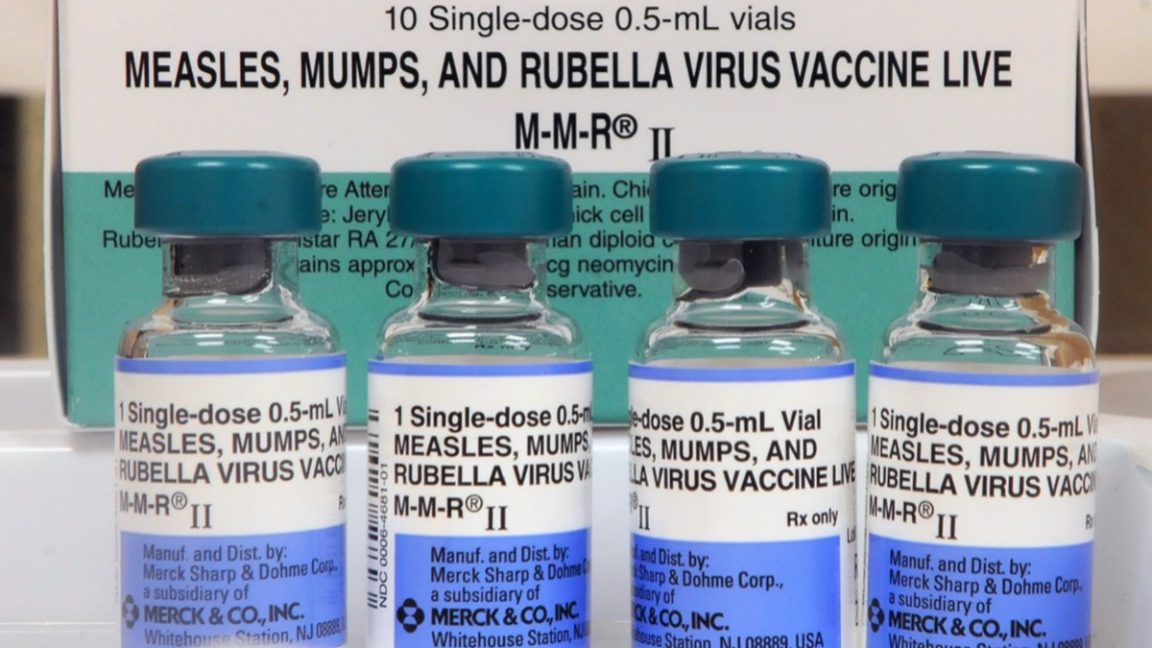
Pennsylvania's explosive measles outbreak is now the largest the US has seen since the highly infectious virus was declared eliminated in 2000. With well over 1,000 cases, it's the largest on record since 1991.
Pennsylvania's health officials reported 1,078 measles cases in all of 2026 as of this afternoon. That includes 12 cases in January and March, with the remaining 1,066 cases since April, when the current outbreak began. The tally includes 145 cases recorded in the last seven days and 74 identified since the previous update on Monday. Health officials noted that 40 of the 74 cases added today were from more than two weeks ago and are just now being recorded.
Among the cases, there have been 207 hospitalizations and five deaths—a newborn, a 6-week-old, an 18-year-old, a 20-year-old, and a 40-year-old. All of the deaths occurred during the current outbreak in people who were unvaccinated; the two infants were too young to have been vaccinated.
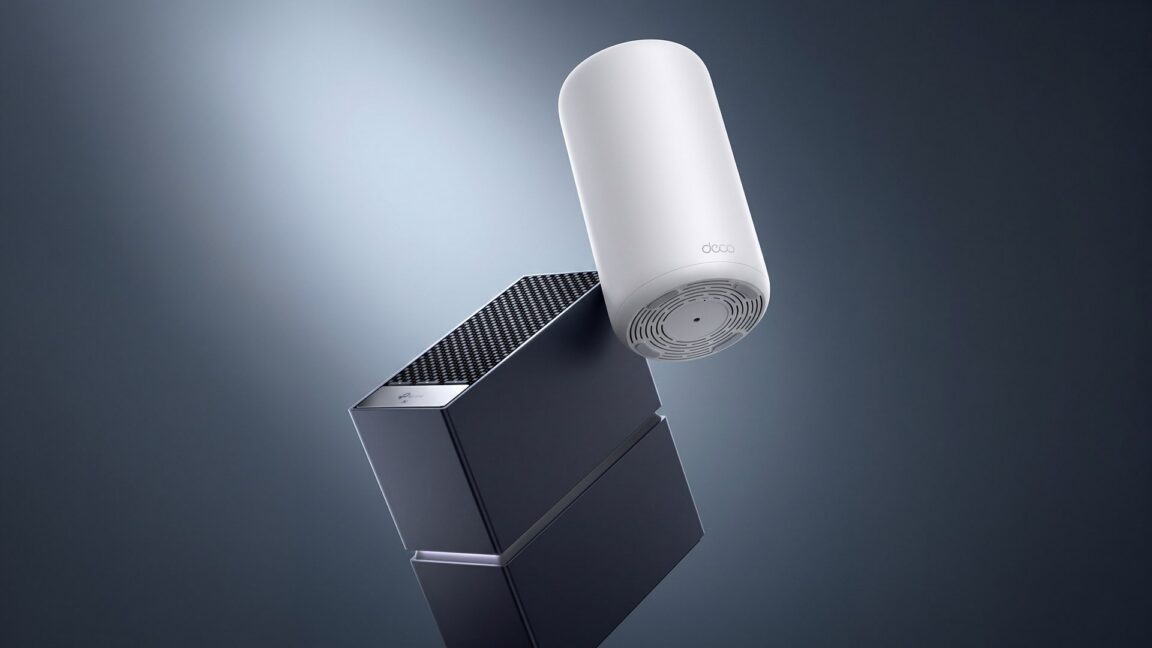
TP-Link is facing more legal troubles in the US as Florida and three other states filed lawsuits alleging that it lied to consumers about its connections to China and the risks of its routers being exploited by Chinese state hackers.
The lawsuits were filed yesterday, about six months after the Federal Communications Commission announced a sweeping ban on consumer-grade routers produced wholly or partly outside of the US. Numerous router makers have obtained exemptions to the ban, but the Trump administration so far has not granted one to TP-Link.
Router makers that received exemptions include Netgear, Asus, Adtran, Amazon and its Eero subsidiary, Calix, Nokia, SpaceX's Starlink division, and others. For now, TP-Link is unable to sell its latest Wi-Fi 8 routers in the US, though models approved before the ban can still be sold.
Life is remarkably selective. Life relies on many molecules with what is termed "handedness"—they're chemically identical but are mirror images of each other. Most chemical reactions will make a 50-50 mix of the left- and right-handed forms of a chemical, but life uses only one of them. In fact, because of the differences between left- and right-handed chemicals, most of the key enzymes used by organisms will fail to work if they're presented with chemicals that have the wrong handedness.
That poses a bit of a challenge for origin-of-life research, as we're forced to explain how a world that may have started with an even mix of left- and right-handed chemicals produced organisms that only used one of them.
Today's Nobel Prize in Chemistry goes to two individuals, Henri Kagan and Kenso Soai, who discovered chemical reactions could be biased, producing large excesses of one of the two forms of a chemical.
As many doctors are moving ahead with the latest advances of modern medicine—from powerful obesity drugs to breakthrough cancer treatments—pediatricians are being forced to turn back, fighting to maintain advances in children's health that were hard-won decades ago.
With anti-vaccine advocate Robert F. Kennedy Jr. as health secretary, the American Academy of Pediatrics (AAP) has spent a considerable amount of time and resources in the past year fiercely defending lifesaving vaccinations—safe, routine shots that have saved the lives of millions of children over decades and thwarted untold suffering and disability.
But just this week, The New York Times reported that Ken Paxton, the attorney general of Texas, has opened aggressive investigations against pediatricians simply because they vaccinated their patients. Paxton falsely claims vaccines are part of a "multi-level, multi-industry scheme." But critics say his anti-vaccine campaign appears more aimed at currying favor with Kennedy, President Trump, and their supporters as Paxton runs for the US Senate.
After pleading guilty, a 54-year-old North Carolina man, Michael Smith, was sentenced to 18 months in prison for using artificial intelligence to generate songs for a scheme that stole millions from music streaming platforms.
In a press release Tuesday, the US Department of Justice said that Smith is the first American criminally charged with AI-assisted streaming fraud.
First charged in 2024, Smith successfully ran the scheme for seven years without detection.
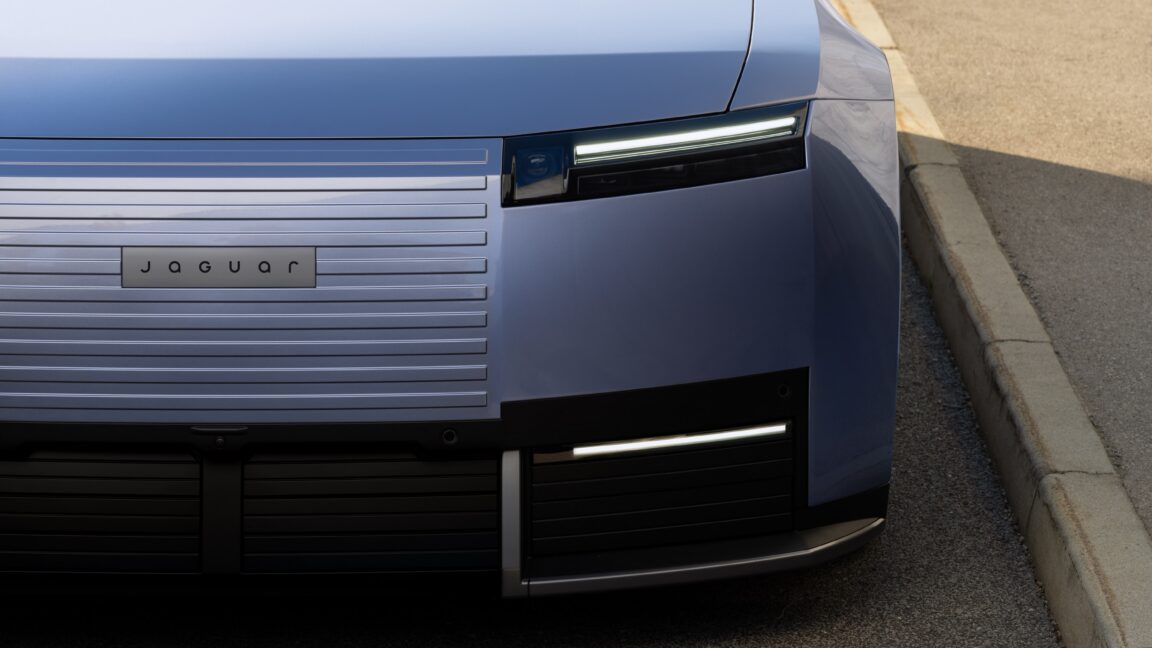
Does it feel like people are perhaps a little grumpier or more on edge these days? It’s not like it’s without reason. There are wars. The climate is going haywire. Someone just died of plague. Scientific research is under attack. Machines keep stealing humans’ work. The media is a mess. And just when it all starts to feel a little overwhelming, Jaguar goes and unveils a new car.
The Type 01 is the first model to arrive from Jaguar’s rebirth. The British carmaker was an early entrant to the modern EV market with the 2017 I-Pace, which was fun to drive even if it was too small inside and perhaps completely unreliable. An all-electric sedan was supposed to be next, but a year from the showroom, it was abruptly canceled, leaving the automaker with nothing to sell as old models like the F-Pace ceased production.
Instead, Jaguar got to work on an all-new electric vehicle platform called JEA, which will underpin an all-electric product line. An elevated ownership experience and a starting price of about double the brand’s previous $60,000 entry point was the idea, Jaguar boss Rawdon Glover told me in 2024. Then last year the brand started teasing its relaunch, and everyone got upset. Things got even worse when the first images of the slab-sided and pastel-shaded Type 00 coupe concept leaked.
One of Donald Trump’s biggest goals as president is to increase domestic manufacturing and reshore supply chains so that the most in-demand technologies in the world can be 100 percent made in the United States.
By executive order last December, he launched his “Genesis Mission,” an ambitious plan seeking to leverage US dominance in AI to maintain or seize an edge in advanced robotics, biotechnology, semiconductors, and nuclear technologies. According to Trump, that plan works best with self-sustaining supply chains. Not even neighboring countries or longtime allies should be relied upon to manufacture a single component of any US product in his ideal world.
The Consumer Technology Association (CTA) has long warned that Trump’s reshoring goals are not grounded in reality, but only recently has America’s largest technology trade association attempted to estimate what it would cost businesses and consumers to follow through on Trump’s plan.
As tensions mount over who gets access to top-end artificial intelligence, French company Mistral has released a new freely available model that it claims can compete with the very best from the US and China.
The new 1 trillion-parameter model, Mistral Large 4—nicknamed Le Chonk—can be used and customized by anyone. It’s currently available in preview, with a final version to follow by the end of the month. Though Le Chonk is built to compete with leading general-purpose models, it’s optimized specifically for coding and cyberdefense, as well as tasks particular to manufacturing, finance, electrical engineering, and other niches.
“There are a lot of areas where the other labs will not focus that much,” Guillaume Lample, cofounder and chief scientist at Mistral, tells WIRED. “There are so many domains in which you can improve models.”
Every piece of AI content from Google's Gemini models has a hidden SynthID label, which makes it very difficult to pass the content off as authentic. SynthID has also gotten buy-in from other major AI players, but actually checking for those invisible watermarks has been a convoluted process. It's going to be a little easier going forward, though. Google has announced that its SynthID detector now supports watermarks from all its partners, and it's available for anyone to use on a new dedicated website.
SynthID is an invisible signal encoded in the pixels of AI-generated images and videos, and in the waveform of AI audio. Google says Gemini alone has integrated SynthID with over 180 billion images and videos, plus 240,000 years of audio. Until now, the only way for those outside of Google's trusted tester program to check for SynthID was to ask Gemini. This is rather clunky, and the model's output could sometimes be confusing when you just wanted a simple "yes" or "no."
Now you can cut Gemini out of the loop. Starting today, you can go to the new SynthID.com website to check a piece of content for an AI watermark. A major limitation of Google's previous detector was that it only checked for Google's version of SynthID. Even though ChatGPT images, for example, have SynthID, they wouldn't be flagged in Google's detector. That's no longer a problem.
There’s been something of a change in the world of motorsport over the past few years. It has to do with where the money comes from. In the old days, it was tobacco and, to a lesser extent, booze. Today such things are mostly banned, and when you look at a racecar covered in sponsor logos, you’re likely to see something crypto-, cyber-, or AI-related.
This makes sense—an ever-larger share of our GDP is wrapped up in those segments. They’re the ones with all the money, and it takes money to go racing. So at the amateur level, we’ve seen tech CEOs replace dentists as the privateer of choice: This past weekend’s Petit Le Mans included co-founders of GitHub, CrowdStrike, Shopify, and the creator of Ruby on Rails, to name a few.
But this is an instance where a sponsor can provide tangible benefits to their motorsports partner beyond a bank transfer, as Chip Ganassi Racing (CGR) and OpenAI have been showing in IndyCar this year.
I found the trailer for Digger intriguing, starring a nearly unrecognizable Tom Cruise and giving off strong Dr. Strangelove vibes. Plus, it is four-time Oscar-winning director Alejandro G. Iñárritu’s (Birdman) first English-language film since 2015’s The Revenant. Those elements quickly moved it near the top of my "must-see" list even if details about the actual plot were lacking. Given Iñárritu’s pedigree, the film seemed poised to be prime Oscar bait.
(Major spoilers appear below the gallery. We'll give you a heads-up when we get there.)
By now it's clear that Digger is on track to be one of the biggest bombs of the year instead, racking up a mere $20 million globally its opening weekend, against a $125 million (possibly more) budget. It has sharply polarized critics and audiences alike, with some appreciating Iñárritu's bold, creative swings and others finding the film practically unwatchable.
It's no surprise that NASA's new tack toward foreign partnerships—good deals only, please—is challenging preconceived notions of international cooperation in space.
Without a massive budget hike, the US space agency's emphasis on building a Moon Base and winning a competition for lunar real estate and resources with China will inevitably leave lesser priorities behind.
Gone is the Lunar Gateway, a space station that was to be assembled in orbit around the Moon. For the United States, Gateway was an unnecessary distraction and expense as NASA goes all-in on placing a surface station near the Moon's south pole.
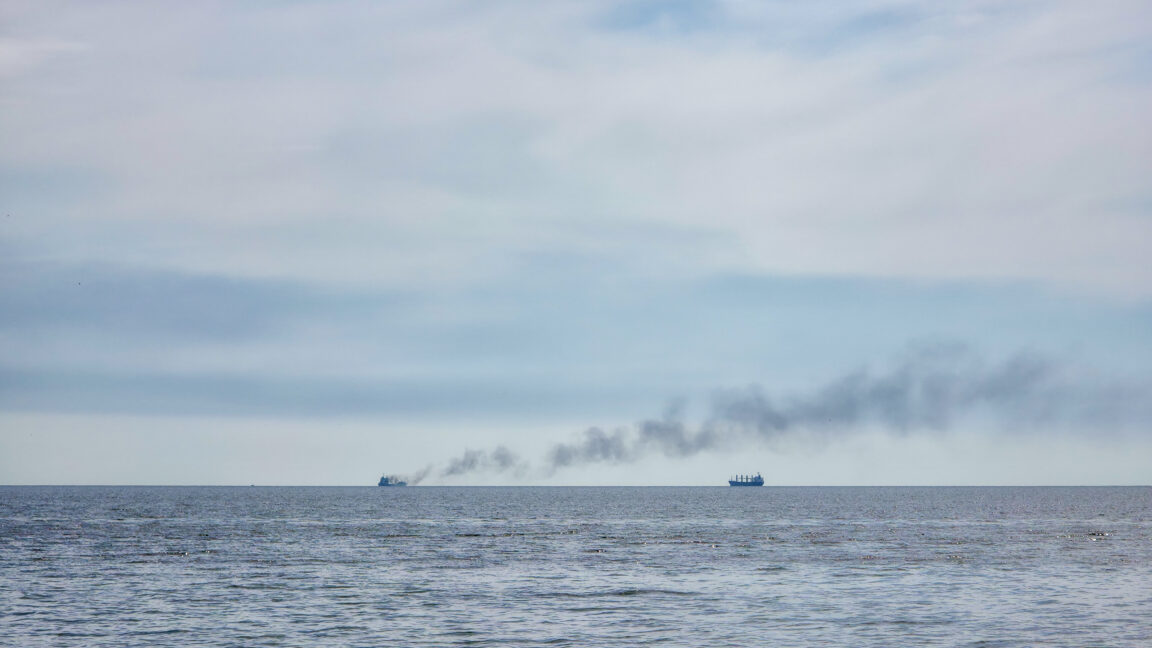
Drones sank two cargo ships and damaged a third in the exclusive economic zones of NATO member countries for the first time, killing at least two sailors. The attacks represent a notable escalation as Black Sea commercial shipping has increasingly come under attack during the Russian invasion of Ukraine, with Russia also being accused of carrying out “hybrid warfare” incidents across Europe.
The Togo-flagged cargo ship Alfa Watan sank, and the Palau-flagged cargo ship Able was set ablaze after being attacked by multiple sea and aerial drones about 80 miles (128 kilometers) off the coast of Bulgaria on October 6, according to the Associated Press. In an interview, Bulgarian Prime Minister Rumen Radev described the incidents as “an unacceptable attack in Bulgaria’s exclusive economic zone” and “a blatant violation of international law and maritime law.”
A Bulgarian ferry managed to evacuate the 18 crew members of the Able, with two severely injured mariners being flown to a hospital in the city of Varna.
OpenAI will begin automatically watermarking text generated with ChatGPT in the European Union, the company has announced. It will also offer the watermarking feature in other regions, but it will be off by default outside of the EU.
The move in Europe is driven by a need to comply with the EU AI Act, which took effect in August. It requires marking content produced by AI models in a way that another tool can detect. Unfortunately, there is still no completely effective and reliable way to do that. A few standards already exist, like SynthID and the C2PA project, but they are relatively easy to circumvent for anyone with basic know-how.
The same is likely true for OpenAI's watermark. Its method is proprietary; the company calls it textGrain, and has published a technical paper explaining how it works. But in general, it works like other LLM watermarking tools we've seen in the past: It puts patterns in the word choices that are not clear to a human reader and that don't meaningfully change the general quality of the output, but that someone with a key can use a specialized detector to find. OpenAI says it will be giving access to the detector to a limited number of researchers and organizations and providing a request-for-approval process for others to be added over time.
After months of industry and customer speculation, Paramount Skydance has shed some light on the future of the HBO Max and Paramount+ streaming services.
In an announcement today, Skydance said that all of the direct-to-consumer streaming services it owns, including the Discovery+ service that Discovery Inc. (which merged with WarnerMedia in 2022 to create WBD) launched in 2021, “will unify into a single service over time.”
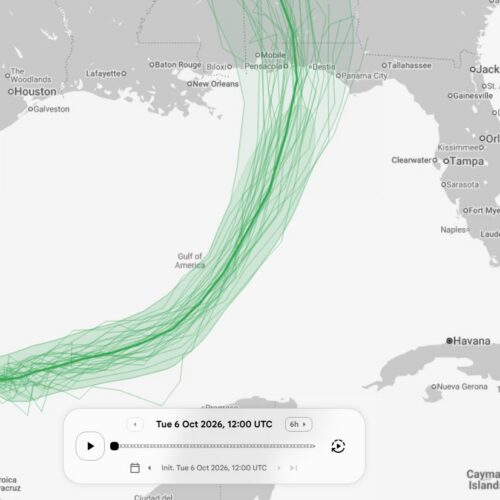
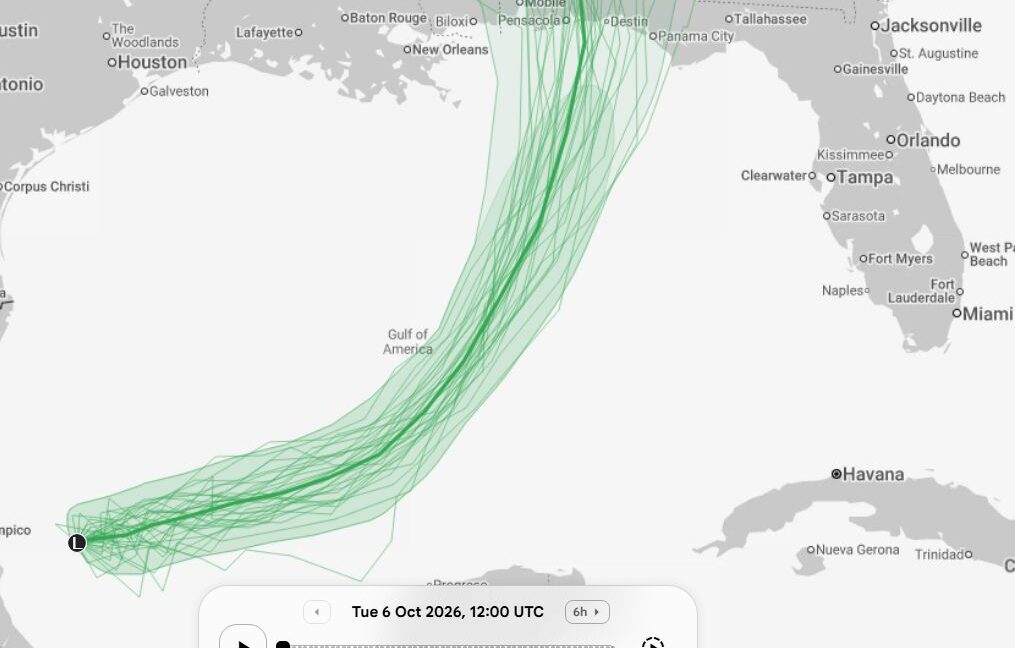
A low-pressure system in the western Gulf of Mexico should soon become a tropical storm, and based on the latest forecast modeling, it has a decent chance of becoming a hurricane.
Normally, a hurricane forming in early October would not be particularly noteworthy. However, this year the development of a hurricane would be a big deal—because it has not happened yet.
In the modern hurricane record—an era dating to about World War II when there has been aircraft reconnaissance and later continuous satellite coverage—there has never been an Atlantic season without a hurricane, and no season has gone this late without one forming.
Attackers hijacked three top-level domains and used their control to mint counterfeit TLS certificates for Google and other large organizations, Google said Tuesday.
The attackers launched a series of attacks on the .gh, .sl, and .as country code top-level domains (ccTLDs) and then modified authoritative DNS records for selected domains within those namespaces. By controlling those DNS records, the attackers were able to pass automated domain control validation checks and obtain unauthorized certificates for “several Google domains” and “several leading global brands and widely used online services.” Google said it updated Chrome to block all certificates it identified as unauthorized, and worked with the issuing certification authorities to ensure the unauthorized certificates for Google properties were revoked.
Certificate issuance: The weak link in the chain
TLS certificates are the cryptographic credentials that underpin authentication and encryption protections for websites, mail servers, and other Internet infrastructure. These x.509 certificates use a digital signature to bind a domain name such as google.com to a public key. The public key is publicly available, while the private key is held only by the website operator. When a connection shows that the keys match, the visiting party knows it’s connected to the authentic site rather than an impostor. Possession of unauthorized certificates allows attackers to cryptographically impersonate the affected infrastructure.
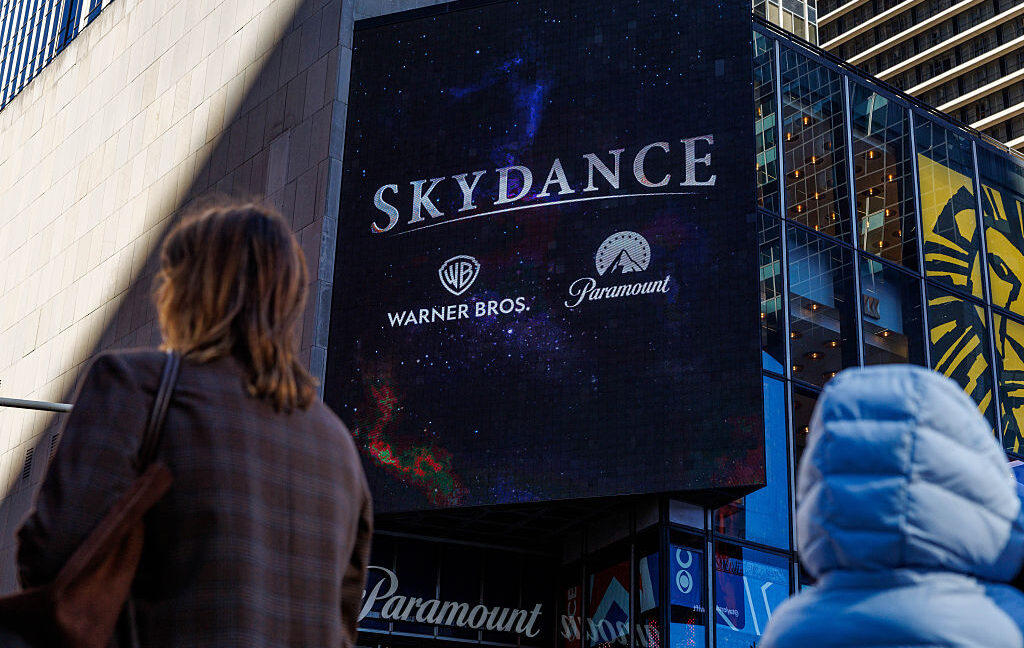
Paramount Skydance completed its $111 billion merger with Warner Bros. Discovery today, after a last-ditch effort to block the deal was rejected by Supreme Court Justice Elena Kagan.
The post-merger company is called Skydance, taking the name of a firm that Paramount bought in a separate deal last year. The new Skydance combines two of the largest movie studios, streaming services Paramount+ and HBO Max, CBS, CNN, "and a portfolio of live sports including CBS Sports and TNT Sports, as well as a deep programming library and expansive collection of brands and franchises," Skydance said today in a press release announcing completion of the deal.
The merger was delayed a bit by a lawsuit filed by California and 11 other states. In July, US District Judge Araceli Martínez-Olguín in the Northern District of California ruled that the combination would likely reduce competition substantially and violate antitrust laws.
When Ars launched in 1998, there was one way to read it: in a web browser on a PC (or Mac). Your screen of choice was either some massive CRT or a very expensive LCD monitor (or, in my case, the less-expensive grayscale, passive-matrix LCD on a PowerBook). Either way, it was butt in chair, chair at desk.
One of the first perks we offered subscribers way back at the turn of the millennium allowed them to read Ars without a browser. Articles were available as formatted PDF files, so you could print out John Siracusa's Mac OS X Public Beta review and read it on the subway or build your own searchable archive of your curated Ars content. Another option was full-text RSS feeds—instead of getting a two-paragraph summary, subscribers could browse Ars in their favorite RSS reader.
It's 2026, and while screens have proliferated in size and portability, ArsPro subscribers still get PDFs of every article and full-text RSS feeds, because sometimes the web isn't always the ideal place to read the web.
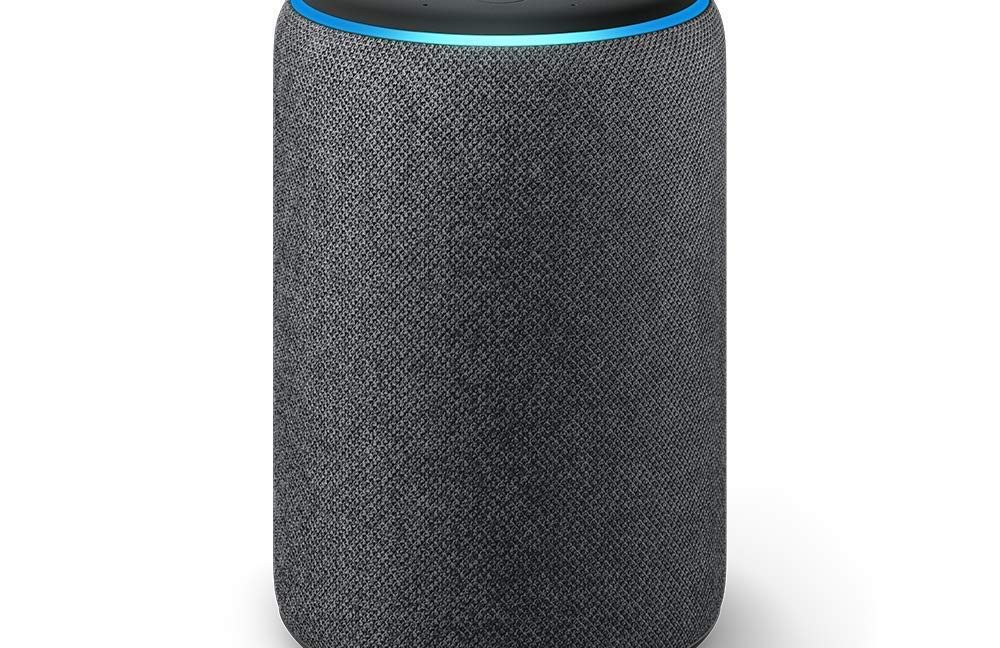
Amazon has disabled Alexa control of devices plugged into the company's Echo smart speaker’s AUX port.
Users have reported receiving an email from Amazon this week informing them of the change. “This is a reminder that as of today, voice commands to control your Echo device’s Aux input are no longer available. Requests like 'Alexa, play from line in” or “Alexa, set aux input' will no longer work,” an email that Amazon sent reads, according to a screenshot a Reddit user shared this week.
An Amazon spokesperson confirmed the news to Ars Technica today.
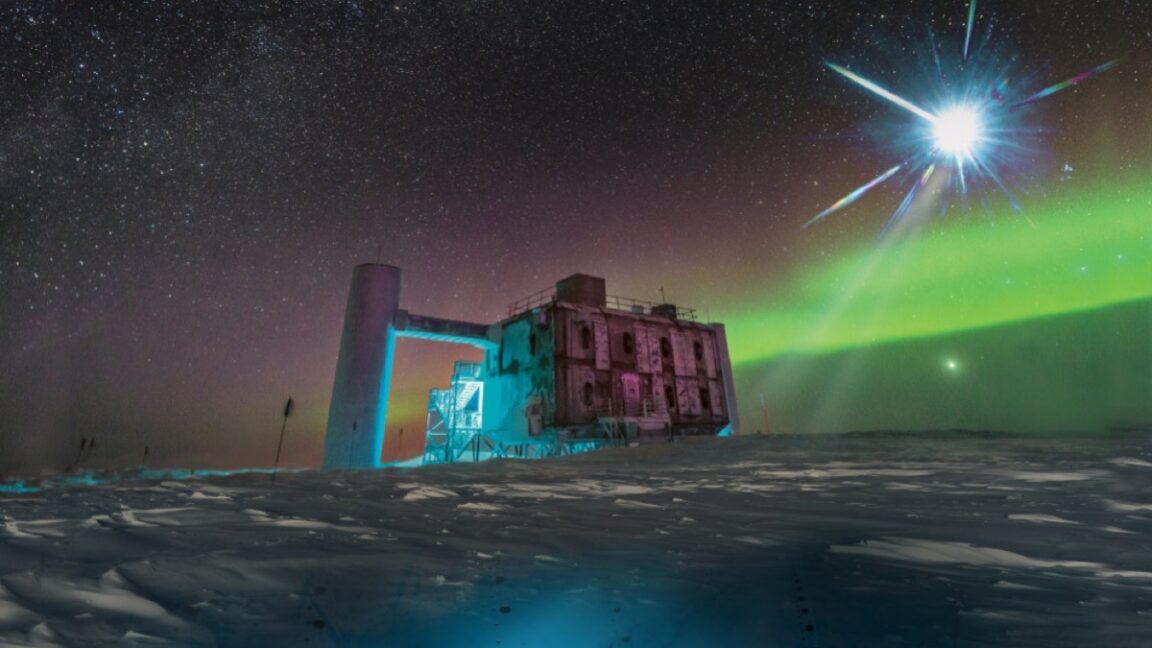
Francis Halzen, a physicist at the University of Wisconsin, Madison, has won the 2026 Nobel Prize in Physics "for decisive contributions to the IceCube Neutrino Observatory and the discovery of high-energy neutrinos of astrophysical origin.” Halzen spearheaded the development and construction of the IceCube Neutrino Observatory in Antarctica, enabling physicists to capture high-energy neutrinos created in the distant universe.
“It was a great surprise, and I obviously didn’t expect it,” Halzen said during a news conference in Stockholm, Sweden, speaking by phone from Italy. While the Nobel was awarded to Halzen, he emphasized that his work was the result of a “large collaboration” with other researchers.
“This reflects on the really courageous people who joined me in this project when really no respectable conservative physicist would have joined me. But many talented people did, and that’s why I’m here,” he said.
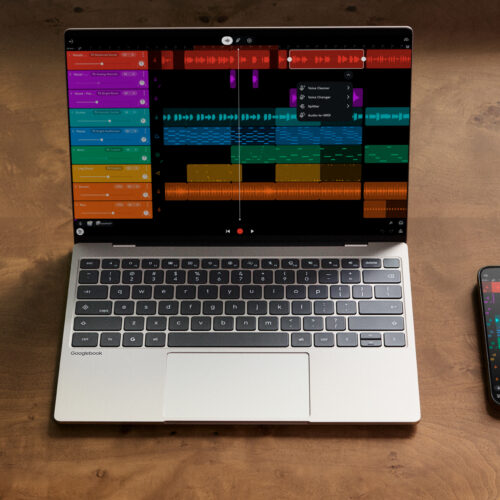
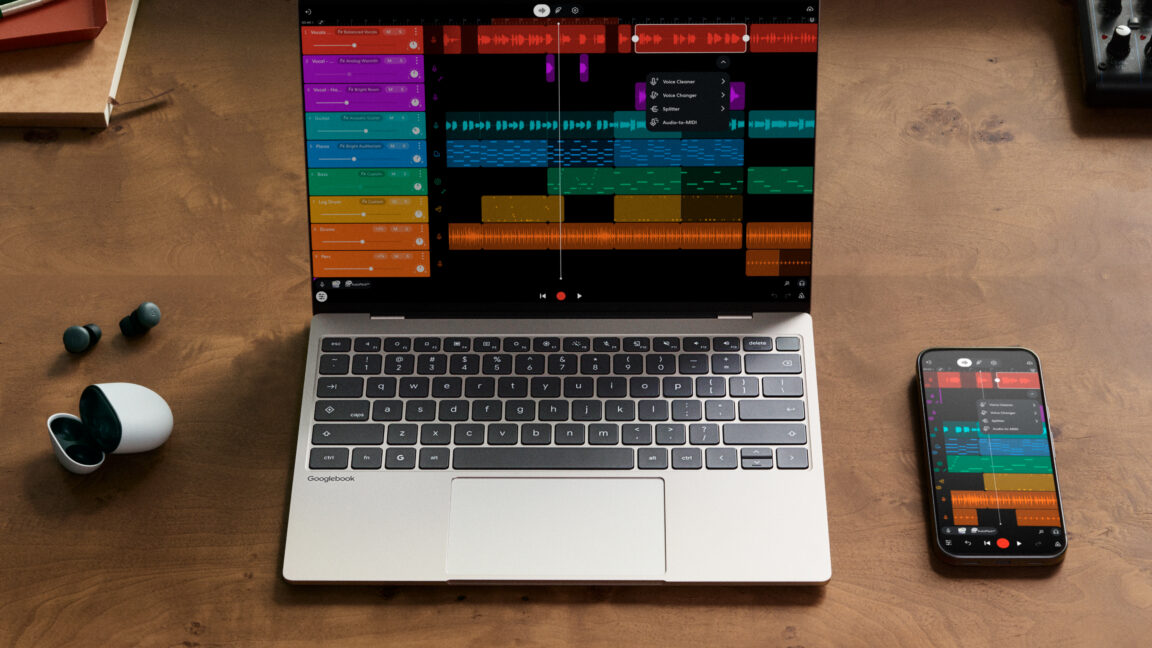
Googlebooks are Google's latest attempt to carve out a piece of the premium laptop market, and tight integration with Android phones is a key part of that effort. Now that Googlebooks are available, we're learning of some frustrating limitations of that plan. For now, Googlebooks will only play nicely with your phone if you have a Pixel.
When Google announced the launch window for Googlebooks, it said the laptops were "engineered to work with your Android phone right out of the box." But as with many things Google, the truth is more convoluted. We have since learned that you need Android 17 for any of the nifty integrations to work. With a compatible Android 17 phone, you can seamlessly stream apps to your laptop, access files on your phone, mirror notifications, and continue where you left off in certain apps when switching from phone to laptop.
You might think that the latest Samsung phones, which shipped with Android 17, would be ready for this experience. You'd be wrong, though. Some early Googlebook adopters have complained that phones like the Z Fold 8 won't work with the laptops. While the devices appear to see each other, the phone doesn't stay connected. Google representatives have sinceconfirmed that these "Better Together" features are not currently supported on even the latest Samsung phones. An update that brings support to Samsung phones will roll out in "the coming weeks."
 Login