❌

Reading view

Topgolf saved over $11.3 million after leaving VMware

Topgolf’s VMware costs were going to increase by 400 percent under Broadcom. To avoid that cost, the sports entertainment company moved 12,000 virtual machines (VMs) to VergeIO’s VergeOS and has saved over $11 million so far.

Before migrating, Topgolf’s VMware connection “ran very deep,” Scott Forehand, Topgolf’s global infrastructure manager, told Ars Technica.

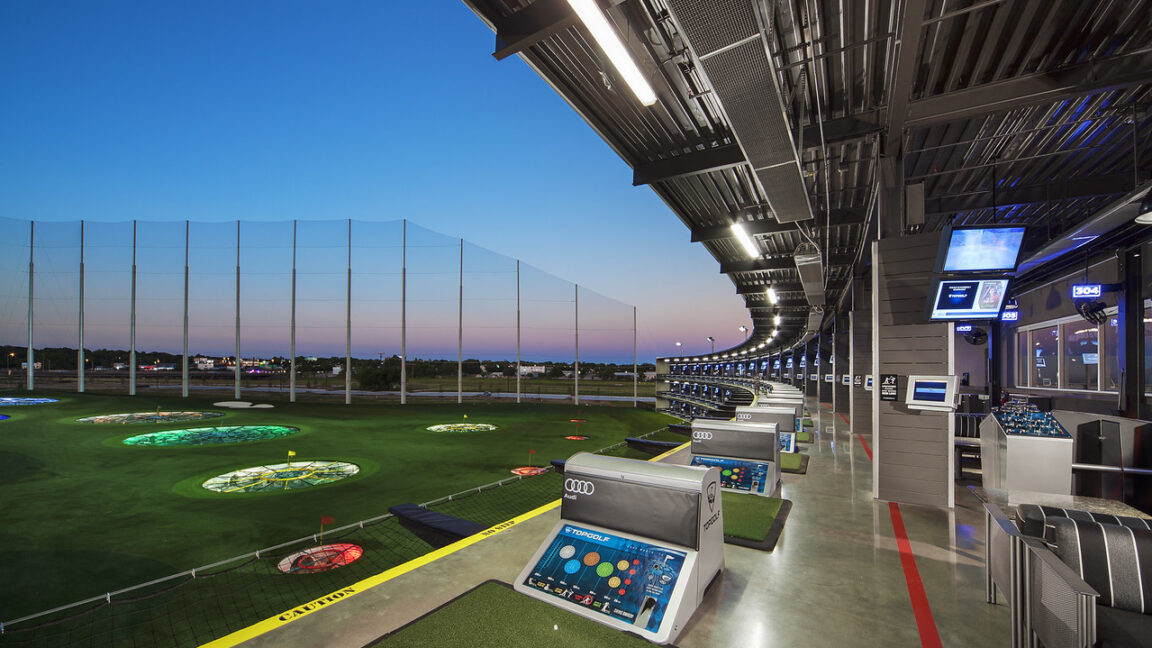
Topgolf has over 100 locations worldwide featuring interactive golf games with real-time shot tracking and digital analytics. The company used vSphere and ESXi for decades and started using VxRail, the hyperconverged infrastructure (HCI) platform that VMware co-engineered with Dell, in 2017. Topgolf employees previously participated in numerous VMware customer councils and have been interviewed for books on how Topgolf used vSphere and Horizon (now Omnissa Horizon), per Forehand, who is a leader of the Dallas/Ft. Worth VMware User Group.
Read full article

Comments

© TopGolf

  •  

PC shipments fall 20.1 percent in “sharpest decline” since Q1 2023

PC shipments saw a steep drop of about 20 percent in Q3 2026, analysts reported this week.

The industry saw its “sharpest decline since “Q1 2023," Omdia said in an announcement toady. Global shipments of laptops, desktops, and workstations fell 21.2 percent year over year (YoY) to 58.1 million devices, the analyst said.

Desktop PC shipments (including desktop workstations) decreased 23.5 percent to 11.7 million units, and laptop shipments (including laptop workstations) declined 20.6 percent to 46.4 million, per Omdia.

Read full article

Comments

© David Paul Morris/Bloomberg via Getty Images

  •  

Hackers obtain counterfeit TLS certificates for Google and other large services

Attackers hijacked three top-level domains and used their control to mint counterfeit TLS certificates for Google and other large organizations, Google said Tuesday.

The attackers launched a series of attacks on the .gh, .sl, and .as country code top-level domains (ccTLDs) and then modified authoritative DNS records for selected domains within those namespaces. By controlling those DNS records, the attackers were able to pass automated domain control validation checks and obtain unauthorized certificates for “several Google domains” and “several leading global brands and widely used online services.” Google said it updated Chrome to block all certificates it identified as unauthorized, and worked with the issuing certification authorities to ensure the unauthorized certificates for Google properties were revoked.

Certificate issuance: The weak link in the chain

TLS certificates are the cryptographic credentials that underpin authentication and encryption protections for websites, mail servers, and other Internet infrastructure. These x.509 certificates use a digital signature to bind a domain name such as google.com to a public key. The public key is publicly available, while the private key is held only by the website operator. When a connection shows that the keys match, the visiting party knows it’s connected to the authentic site rather than an impostor. Possession of unauthorized certificates allows attackers to cryptographically impersonate the affected infrastructure.

Read full article

Comments

© Getty Images

  •  
❌